Whitelist
Allowlist of IPs, IP ranges, ASNs and player usernames that bypasses every filtering layer — anti-bot, Anti-VPN, Country, ASN.
The Whitelist is a bypass list of IPs, IP ranges, ASNs and player usernames. Entries on this list skip every filtering layer — anti-bot, Anti-VPN, Country filter, ASN filter — and connect straight through to your backend.
Where to find it
Open Network → Settings → Filtering → Whitelist.

The toggle at the top right turns the whole whitelist on or off without deleting its entries.
What it bypasses
A whitelisted entry is exempt from:
- Anti-bot challenges (no rejoin prompt, no Hardcore web verification).
- Anti-VPN detection — the IP is accepted even if it sits in a known VPN range.
- Country filter — the IP connects regardless of the country list.
- ASN filter — the IP connects regardless of ASN block rules.
What it does not bypass:
- L3/L4 mitigation at the edge — volumetric floods are still dropped before they reach the application layer, for everyone.
- Per-IP rate limits that protect against single-source packet floods.
When to add an entry
- A staff member whose IP keeps getting flagged by Anti-VPN or Country — whitelist their IP, or their username.
- A specific player whose home ISP is on the ASN block list.
- Your office or a partner’s network — whitelist its IP range.
- An entire ISP / hoster you want to keep accepted even when you tighten the filters — whitelist its ASN.
Adding an entry
Click Add to whitelist, pick the Entry type, type the Value, optionally a short Note (up to 16 characters, e.g. who it is), and click Add.
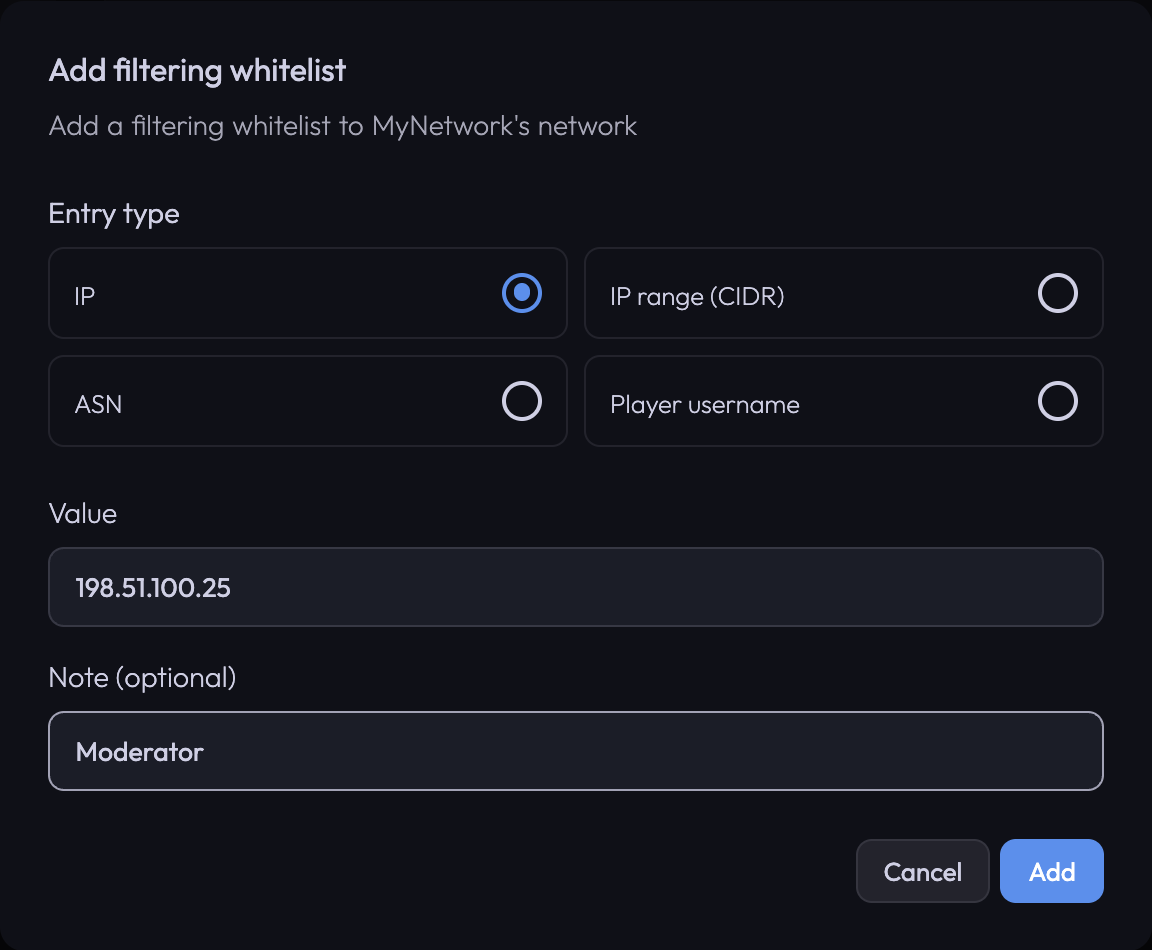
IP One IPv4 or IPv6 address. Example: 203.0.113.10 or 2001:db8::1.
IP range (CIDR) A whole range of IPs in CIDR notation. Example: 198.51.100.0/24 or 2a01:e0a::/32.
ASN An autonomous system number, digits only (no AS prefix). Example: 16276 for OVH.
Player username A Java Edition username: 3 to 16 letters, digits or underscores. Example: Notch.
The panel checks the value against the type you picked and refuses anything that doesn’t match (for example an IP range typed as an IP).
Adding an IP
Pick IP and type an IPv4 or IPv6 address — e.g. 203.0.113.10 or 2001:db8::1. For a whole range, use IP range (CIDR) instead.
Adding an IP range
Pick IP range (CIDR) and type the range in CIDR notation: 198.51.100.0/24 covers 198.51.100.0 to 198.51.100.255. IPv6 ranges work the same way (2a01:e0a::/32).
Adding an ASN
Pick ASN and type the ASN number without the AS prefix. For OVH (AS16276) you’d type 16276, for Amazon AWS 16509, for DigitalOcean 14061, and so on.
Whitelisting an ASN exempts every IP in that autonomous system from the filters — useful to keep a whole ISP trusted without listing every customer IP.
Adding a player username
Pick Player username and type the player’s Java Edition username (3 to 16 letters, digits or _). That player bypasses the filters whatever IP they connect from — handy for staff members on the move.
Removing entries
Click the delete icon on the row. The change is immediate; existing connections from the affected IPs aren’t dropped. Use the edit icon to change an entry’s type, value or note.
What’s next
Last updated: October 22, 2026